A Devastating Breach of Public Trust
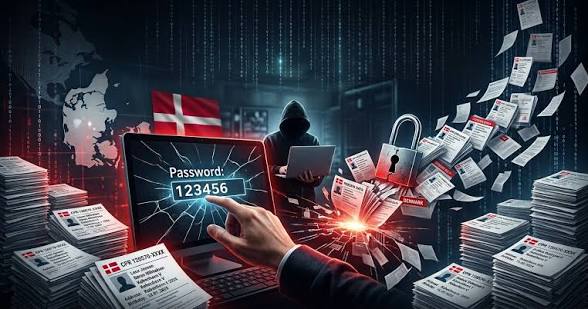
In one of the most alarming cybersecurity failures in recent Scandinavian history, a massive data exposure has compromised the central registry numbers of vast numbers of Danish citizens. The culprit behind this devastating leak was not a sophisticated state-sponsored threat group armed with zero-day exploits, nor was it a complex cryptographic flaw. Instead, investigators revealed that an administrative account guarding sensitive identity infrastructure was secured using '123456'—a password that has consistently topped lists of the world's worst login credentials for over a decade.
The Central Person Register, commonly known as the CPR system in Denmark, is the backbone of modern civil administration across the nation. A CPR number is a unique ten-digit identifier assigned to every resident at birth or upon receiving permanent residency. It serves as the primary key connecting an individual's medical records, tax filings, banking relationships, property deeds, and employment history. In a country praised worldwide for its seamless digital government services, compromising the CPR system strikes directly at the core of national digital infrastructure.
While the full scale of the incident continues to unfold, initial reports indicate that unauthorized entities gained prolonged, unchecked access to internal databases. The exposure of these personal identifiers opens the door to widespread identity theft, targeted spear-phishing campaigns, and administrative fraud that could plague affected citizens for years to come.
The Anatomy of an Avoidable Security Failure
To understand how an administrative endpoint was left protected by '123456', one must look at the common systemic issues that plague large public-sector IT systems. Over decades of modernization, national registries often become web-like ecosystems composed of legacy databases, third-party vendor integrations, testing environments, and localized municipal access portals. While primary systems might boast state-of-the-art authentication protocols, peripheral or staging systems frequently slip through technical governance cracks.
Preliminary details suggest that the breached account was linked to an intermediate system or service account used for data synchronization or internal testing. In many organizations, developers or IT administrators create accounts with temporary, simple passwords during setup phases with the intention of replacing them before deployment. When documentation fails or project handovers occur without strict audits, these insecure access points remain active in production environments—waiting silently for automated scanners to discover them.
Attackers today rarely waste time manually guessing passwords on high-profile targets. Instead, threat actors run automated scripts across known IP ranges, constantly attempting default and high-frequency credentials like '123456', 'password', or 'admin' against open ports and login endpoints. Once an automated tool hits a valid combination, it alerts human operators who then move laterally through the network to extract data or elevate privileges.
The Critical Role of Denmark's CPR System
The severity of this breach cannot be overstated given the structural role CPR numbers play in daily Danish life. Unlike social security numbers in some countries, which were originally designed solely for retirement benefits and later retrofitted as identity keys, the CPR system was built from the ground up to integrate civil services seamlessly.
In Denmark, almost every interactions with private and public entities requires a CPR identifier. Healthcare workers use it to pull electronic medical records; banks use it for mandatory Know Your Customer (KYC) verification; telecom providers require it to issue mobile plans; and landlords use it to complete rental agreements. It is the connective tissue of Denmark's trusted digital ecosystem.
Because the CPR number was designed under the assumption that surrounding verification layers—such as official identity cards or multi-factor digital tokens like MitID—would validate the user's identity, the number itself was often treated as semi-confidential rather than strictly secret. However, when malicious actors possess a citizen's full name, address, and CPR number simultaneously, bypassing security questions, opening fraudulent lines of credit, or executing sophisticated social engineering attacks becomes drastically easier.
Why Basic Credential Hygiene Keeps Failing
This incident highlights a frustrating reality in modern cybersecurity: despite billions of dollars spent annually on advanced artificial intelligence detection systems, zero-trust architectures, and end-point protection, human error and basic hygiene failures remain the primary vector for major breaches.
Several structural organizational issues explain why bad passwords persist across major institutions:
- Shadow IT and Unmonitored Endpoints: Departments frequently deploy software solutions or cloud instances without consulting centralized security teams. These unmonitored systems lack enforced security policies.
- Absence of Password Complexity Policies: If an identity management system does not programmatically block common strings or enforce minimum length requirements, users will inevitably choose options that are easy to remember.
- Lack of Multi-Factor Authentication (MFA): A weak password becomes significantly less dangerous if access requires a second factor, such as a hardware token or an authenticator app code. Leaving administrative portals accessible via single-factor authentication represents a fundamental breakdown of baseline security standards.
- Failure of Identity Governance and Administration (IGA): Accounts created for former employees, temporary contractors, or specific past projects are often left active indefinitely, creating an expanding attack surface over time.
Immediate Remedies and Long-Term Technical Mandates
Following the discovery of the breach, regulatory bodies and IT administrators faced immediate pressure to contain the damage and restore public trust. Beyond revoking the compromised credentials and auditing system access logs, the incident calls for fundamental changes in how sensitive public sector databases are safeguarded.
First, public institutions must enforce automated credential checking against compromised password databases. Open-source resources and commercial tools allow organizations to continuously screen user credentials against known breach lists, preventing anyone from setting easily guessable strings like '123456'.
Second, absolute enforcement of Multi-Factor Authentication (MFA) across all administrative, developer, and service accounts is non-negotiable. Modern security frameworks dictate that no single password, regardless of its length or complexity, should grant access to sensitive databases containing personal citizen data.
Third, network segmentation and Zero Trust Architecture (ZTA) must be rigorously implemented. Even if an attacker successfully guesses a password on a peripheral account, strict internal segmentation should prevent that account from querying or exfiltrating core production databases like the CPR registry.
Lessons for the Global Tech and Security Community
The Danish CPR data breach serves as a stark reminder for security leaders worldwide. High-tech defense mechanisms mean very little if fundamental security controls are overlooked. As public services around the globe continue to digitize rapidly, the reliance on interconnected identity numbers will only grow.
Organizations must move away from viewing cybersecurity as merely an investment in software tools and focus equally on operational governance, automated configuration auditing, and strict identity management policies. For Denmark, rebuilding total confidence in its civil infrastructure will require transparent communication, thorough technical retrofits, and a firm commitment to ensuring that basic oversights never again compromise citizen privacy.