Enterprise cybersecurity teams across North America and Europe are confronting a subtle yet potent threat to corporate identity management systems. A newly discovered phishing framework, tracked by threat intelligence researchers under the moniker N0va, has emerged as a major tool for cybercriminals seeking entry into high-value corporate networks. Unlike traditional phishing kits that rely heavily on deploying payloads or harvesting basic static passwords, the N0va kit focuses on manipulating modern authentication architectures, hijacking valid sessions, and leveraging trusted cloud services to quietly subvert identity controls.
As organizations have migrated their operations to the cloud and enforced multi-factor authentication (MFA) to protect their perimeters, cybercriminals have adapted. Kits like N0va represent the latest evolution in adversary-in-the-middle (AiTM) techniques, designed specifically to sidestep advanced identity security measures. By targeting corporate identity providers and abusing legitimate single sign-on (SSO) workflows, N0va allows threat actors to gain persistence in enterprise environments while generating minimal telemetry on traditional endpoint detection platforms.
The Mechanics Behind the N0va Phishkit
At its core, the N0va phishkit operates as a proxy server positioned between a target user and an authentic corporate login portal. When an unsuspecting employee clicks a malicious link—often distributed through carefully crafted spear-phishing emails or compromised third-party messaging channels—they are directed to a landing page hosted on infrastructure controlled by the attacker. However, instead of displaying a static clone of a login page, N0va dynamically fetches and mirrors the real-time login screen of the targeted service, such as Microsoft 365, Okta, or Google Workspace.
Because the page presented to the victim is a live reflection of the actual authentication portal, all native security prompts function as expected. When the user enters their credentials, N0va relays those details to the legitimate authentication endpoint in real time. If the target organization enforces time-based one-time passwords (TOTP) or push notifications for multi-factor authentication, the system prompts the user for this secondary verification step. The victim completes the prompt, believing they are logging into a benign corporate application.
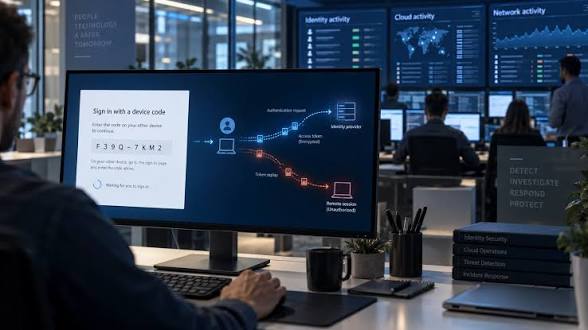
Once the genuine identity provider validates the login, it issues session tokens and authentication cookies back to the user's browser. It is at this critical juncture that N0va completes its hijack. The proxy intercepts these high-value session tokens, records them on attacker-controlled servers, and then forwards the traffic to the actual destination. To the end user, the process appears entirely normal, ending in a successful sign-in. To the attacker, the intercept yields a fully authenticated, active session that completely bypasses the need to solve future MFA prompts during the lifetime of the session token.
Targeting Strategic Regions and Key Verticals
The distribution of N0va campaigns indicates a calculated effort to breach mid-market and enterprise-level organizations across North America and Western Europe. Security researchers analyzing the telemetry associated with these attacks note that the operators behind N0va are primarily focusing on financial services, technology vendors, legal firms, and manufacturing entities. These sectors are frequently targeted due to their heavy reliance on interconnected cloud supply chains and the high commercial value of their intellectual property and operational data.
Attackers utilizing N0va demonstrate significant operational maturity. Phishing lures are often customized to match specific ongoing business processes within target regions. For instance, European targets have received localized lures referencing regulatory compliance updates, regional banking invoices, or local logistics notifications. In North America, campaigns frequently leverage lures disguised as urgent executive requests, internal HR policy reviews, or software access renewals.
Furthermore, the operators behind N0va employ sophisticated traffic distribution systems (TDS) and cloaking mechanisms. Before serving the phishing landing page, the N0va infrastructure evaluates the incoming request. Requests originating from known cybersecurity vendor IP ranges, cloud sandbox environments, or automated security crawlers are served benign content or redirected to harmless search engines. Only traffic that matches specific criteria—such as a valid residential or commercial ISP geolocation and matching user-agent strings—is served the active phishing proxy. This level of defense evasion significantly increases the operational lifespan of N0va deployment domains.
The Cascading Risk of Compromised Enterprise Identities
The true danger of the N0va phishkit lies in what happens after a successful interception. In a modern cloud-centric corporate environment, an authenticated user identity is effectively the new network perimeter. Once an attacker captures a valid session cookie, they do not need to execute malicious binaries on an endpoint or perform noisy lateral movement techniques that might trigger an Endpoint Detection and Response (EDR) agent.
With a stolen session token, an attacker can simply import the authentication state into their own browser and access corporate cloud resources as if they were the legitimate employee. From this initial foothold, threat actors can pursue several post-compromise objectives:
- Persistent Identity Access: Attackers can register their own secondary authentication devices or OAuth applications under the compromised user's profile, ensuring long-term access even if the primary session token expires.
- Supply Chain and Email Hijacking: By accessing the victim's email inbox and internal chat tools (such as Microsoft Teams or Slack), attackers can monitor internal communications, conduct internal spear-phishing campaigns, or interject malicious payment instructions into existing vendor conversation threads.
- Data Exfiltration: Threat actors can systematically crawl connected cloud storage repositories, such as SharePoint, OneDrive, or Google Drive, downloading sensitive financial documents, customer databases, and proprietary source code.
- Cloud Infrastructure Manipulation: If the compromised identity belongs to an IT administrator or DevOps engineer, the attacker can move laterally into cloud management consoles (such as AWS, Azure, or Google Cloud Platform), creating backdoor accounts, spinning up unauthorized infrastructure, or tampering with deployment pipelines.
Why Traditional Defensive Controls Fall Short
The rise of N0va highlights a growing mismatch between traditional cybersecurity defenses and modern, identity-focused attack vectors. For years, enterprise security awareness training has instructed employees to look for subtle signs of phishing, such as incorrect domain names, broken lock icons, or static web forms. However, because N0va acts as a real-time proxy, the authentication screens look pixel-perfect, and attackers frequently host these proxies behind legitimate cloud domain services or subdomains compromised through DNS hijacking, making visual detection nearly impossible for the average worker.
Furthermore, classic multi-factor authentication mechanisms—specifically SMS-based codes, email verification links, and mobile app push notifications—are fundamentally vulnerable to AiTM proxy architectures. Because the human victim is actively interacting with the prompt, they unknowingly complete the verification step on behalf of the attacker's proxy. Relying solely on basic MFA is no longer sufficient to guarantee the integrity of an authenticated session.
Network security devices and email gateways also face limitations when encountering N0va campaigns. Because the initial contact links are often hosted on reputable infrastructure or obfuscated through multiple shorteners and redirects, automated email scanners struggle to flag the messages prior to delivery. Once the victim lands on the proxy, the traffic between the client and the authentic identity provider is fully encrypted via TLS, preventing deep packet inspection without active SSL decryption proxies.
Mitigating the N0va Threat: Modern Identity Security Strategies
Defending against proxy-based phishing frameworks like N0va requires a fundamental shift toward phishing-resistant identity architecture. Organizations relying on legacy authentication frameworks must modernize their access controls to mitigate the operational risks posed by AiTM phishkits.
1. Mandating Phishing-Resistant MFA
The most effective technical countermeasure against N0va and similar phishkits is the implementation of FIDO2/WebAuthn-based multi-factor authentication, such as hardware security keys (e.g., YubiKeys) or platform authenticators like Windows Hello and Apple Touch ID/Face ID. FIDO2 protocols bind the authentication process directly to the specific domain name in the browser's address bar. If a user attempts to authenticate on a N0va proxy domain (e.g., login.company-verify.com instead of login.company.com), the browser recognizes the domain mismatch and refuses to pass the cryptographic credentials, rendering the phishing attack entirely ineffective.
2. Implementing Identity-Aware Conditional Access
Security teams must enforce strict, risk-based conditional access policies within their identity providers. Authentication attempts should be evaluated using contextual signals, including device compliance states, baseline user locations, and IP reputation. For example, managed device policies should require that a session token only be issued if the request originates from an endpoint that is actively enrolled in and verified by the company's Mobile Device Management (MDM) solution. Even if N0va captures a session token, the attacker will be unable to use it from an unmanaged, external device.
3. Monitoring for Token Theft and Session Anomalies
Modern Security Operations Centers (SOCs) must monitor identity provider logs for indicators of session hijacking. Anomalies such as "impossible travel" (e.g., a single user account showing active sessions from two geographically distant locations within a short time frame), rapid changes in user-agent strings, or access requests originating from known TOR exit nodes or anonymizing proxies should trigger automated token revocation and account containment workflows.
4. Shortening Session Durations and Enforcing Continuous Auth
Reducing the lifetime of operational session tokens limits the window of opportunity for an attacker operating with intercepted cookies. Additionally, implementing Continuous Access Evaluation (CAE) standards allows identity providers to revoke active session tokens in real time if a high-risk security event is detected, such as a password reset, account status change, or anomalous network location change.
The Future of Identity Threat Exposure
The emergence and widespread distribution of the N0va phishkit underscores a broader trend in the threat landscape: identity has become the primary attack surface for modern enterprise breaches. As defensive tools make payload delivery and endpoint exploitation increasingly difficult, threat actors will continue to invest heavily in refining methods that exploit human trust and authentication logic.
For enterprise CISOs and IT leaders across North America and Europe, N0va serves as a clear signal that basic security hygiene—such as enforcing legacy MFA and relying on email filtering—is no longer enough to protect corporate assets. Neutralizing the threat posed by advanced phishkits requires a comprehensive transition to zero-trust architecture, the rapid adoption of FIDO2 phishing-resistant credentials, and continuous, telemetry-driven monitoring of cloud identity environments. Until these modern standards become the default baseline across Western enterprise networks, kits like N0va will remain a favored and effective vector for initial corporate access.