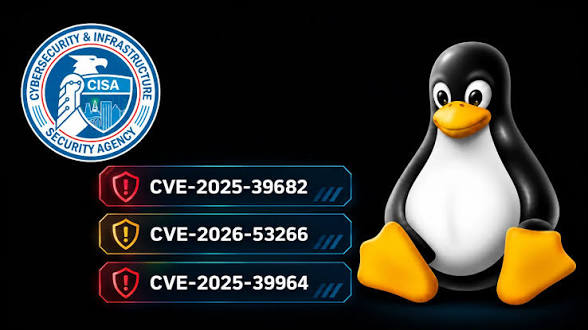
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities (KEV) catalog, raising the alarm over three security flaws affecting the Linux kernel that are actively being weaponized in the wild. Among the newly cataloged threats is CVE-2025-39682, a critical flaw residing within the kernel's Transport Layer Security (TLS) receive path that carries a maximum CVSS severity score of 9.8.
Because the Linux kernel serves as the fundamental bedrock for public cloud environments, enterprise servers, supercomputers, and critical infrastructure networks worldwide, kernel-level vulnerabilities present an immediate threat to global organizational security. The mandatory federal binding directive accompanying CISA's warning underscores the urgency, compelling federal civilian executive branch agencies to patch affected systems within strict deadlines to mitigate potential compromise.
Understanding the Kernel TLS Receive Path Flaw
The most alarming entry in this batch of vulnerabilities is CVE-2025-39682, which addresses an improper handling of unusual or exceptional conditions inside the Linux kernel’s in-kernel TLS (kTLS) implementation. Introduced to offload symmetric encryption and decryption tasks directly to the kernel layer to optimize high-performance network throughput, kTLS significantly reduces the user-to-kernel space context switches typically required for encrypted traffic.
However, implementing complex cryptographic handshakes and state management at the kernel level introduces a dense attack surface. The flaw in question stems from an improper validation check during the receive path of encrypted data streams. When a malicious remote actor crafts specific, out-of-order, or malformed TCP packets wrapped in TLS data, the kernel fails to gracefully process the exception state.
This improperly managed state can lead to severe memory corruption issues, potentially granting an unauthenticated attacker the ability to execute arbitrary code with maximum system privileges—effectively gaining complete root control over the host operating system without requiring local access credentials. Given its near-perfect CVSS score of 9.8, the vulnerability represents a worst-case scenario for system administrators managing exposed Linux infrastructure.
A Growing Pattern of In-Kernel Network Exploits
While Linux has historically enjoyed a reputation for robust security due to its open-source peer review model, the complexity of modern enterprise networking features has introduced fresh challenges. The push over the past decade to integrate performance-enhancing modules, such as kernel-level socket filters, eBPF, and in-kernel TLS, has shifted significant network protocol processing out of user space.
When vulnerabilities manifest in traditional user-space web servers like Nginx or Apache, a successful compromise often confines the adversary within a restricted user context or a container sandbox. In stark contrast, when a flaw lives within the kernel's network stack itself, security boundaries collapse immediately. An exploit executing inside the kernel bypasses standard user-space isolation mechanisms, render-ring containerization frameworks like Docker or Kubernetes largely ineffective at containing the blast radius.
Cybercriminals and state-sponsored threat groups have increasingly focused their research on these low-level network components. By targeting features that process untrusted external data before application-level authentication can occur, attackers secure remote code execution pathways that operate entirely under the radar of traditional endpoint detection and response (EDR) agents.
The Strategic Importance of the KEV Catalog
CISA's Known Exploited Vulnerabilities catalog has emerged as one of the cyber defense community's most authoritative resources. Unlike public vulnerability databases that rely solely on theoretical severity metrics, the KEV catalog requires concrete evidence that malicious actors are actively deploying exploits against live target systems.
When CISA adds bugs to this list, it triggers Binding Operational Directive (BOD) 22-01 for U.S. Federal Civilian Executive Branch (FCEB) agencies. This mandate obligates federal organizations to remediate the highlighted vulnerabilities by a designated due date. While the directive strictly applies to federal entities, private sector enterprises, managed service providers, and foreign governments routinely monitor the KEV catalog as a prioritized roadmap for emergency patching.
The inclusion of kernel-level bugs is a distinct signal that threat actors have successfully operationalized reliable exploit chains. Passive scanning for vulnerable network interfaces is likely already underway across major public cloud providers, making immediate remediation essential for organizational security teams.
Mitigating the Risk Across Enterprise Enclaves
Remediating kernel-level vulnerabilities presents unique operational hurdles compared to updating standard application software. Upgrading a operating system kernel typically requires a full system reboot, a requirement that enterprise IT departments often delay to maintain high availability SLA guarantees for critical business applications.
To address these risks effectively, system administrators and security operations centers should adopt a prioritized response strategy:
-
Identify Exposed kTLS Configurations: Audit all facing systems to identify whether in-kernel TLS acceleration is active. System administrators can check running kernel modules and inspect network stack configurations to pinpoint vulnerable instances.
-
Apply Live Patching Mechanisms: Where zero-downtime requirements prevent immediate system reboots, enterprise organizations should leverage live-patching technologies such as Canonical Livepatch, Red Hat Enterprise Linux Live Patching, or Oracle Ksplice. These tools insert fixes into running kernel memory without disrupting active operations.
-
Deploy Network-Level Safeguards: Web Application Firewalls (WAFs) and Intrusion Prevention Systems (IPS) should be updated with rules designed to inspect and drop anomalous TLS traffic patterns that attempt to trigger state-handling errors on exposed endpoints.
-
Enforce Container Isolation and Kernel Hardening: Ensure that host operating systems utilize security modules like SELinux or AppArmor in enforcing mode to restrict what compromised processes can perform, even if a low-level boundary is breached.
Broader Implications for Infrastructure Security
The active exploitation of these Linux kernel vulnerabilities highlights a persistent tension in modern infrastructure engineering: the trade-off between ultra-low latency performance and security assurance. As enterprise applications handle unprecedented volumes of encrypted traffic, pushing cryptographic tasks deep into the operating system architecture offers necessary speed gains, but at the cost of expanding the critical attack surface.
Moving forward, the security community must continue to evaluate kernel-level feature additions with rigorous automated fuzzing, formal verification techniques, and memory-safe implementation models. Until live systems are updated with the latest vendor patches, security operations teams should treat any unpatched Linux host exposed directly to the internet as a high-risk target requiring immediate isolation and remediation.