A Deadly Convergence of Zero-Days
In the realm of advanced cyber espionage, discovering a single zero-day vulnerability is often considered a major achievement for an intelligence agency or a hacking collective. Combining two separate zero-day flaws into a seamless, weaponized execution chain, however, represents an entirely higher tier of technical mastery and resource investment. That is precisely what cybersecurity researchers discovered during a recently uncovered espionage operation attributed to a state-sponsored threat group linked to China.
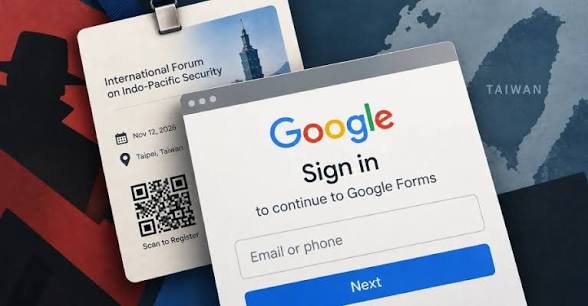
According to new findings from threat intelligence firm Volexity, a threat actor tracked as UTA0560 engaged in a highly targeted spear-phishing campaign that leveraged unpatched vulnerabilities in both Google Chrome and Microsoft Windows. By stitching together an exploit for the web browser with an elevation-of-privilege flaw in the underlying operating system, the attackers bypassed modern sandbox defenses and established persistence on target systems. The ultimate payload of this complex assault was a newly discovered JavaScript-based backdoor designated as GRIMWEDGE.
The attack targeted non-governmental organizations (NGOs) and diplomatic entities, emphasizing the persistent geopolitical motivations behind these campaigns. While software vendors moved quickly to patch the underlying flaws after learning of the active exploits, the incident serves as a stark reminder of the fragile state of enterprise defense against adversaries equipped with multi-stage exploit chains.
Anatomy of the Exploit Chain
To understand why this campaign succeeded where traditional defenses failed, one must analyze how modern web browsers interact with host operating systems. Google Chrome utilizes a sophisticated architecture designed to isolate web contents from the rest of the machine. The browser renderer, which interprets HTML, CSS, and JavaScript, operates inside a restricted sandbox environment. Even if a threat actor manages to compromise the renderer via a browser exploit, they remain trapped inside this sandbox, unable to write files to the hard drive, read system memory, or execute system-level commands.
To escape this confinement, attackers require a secondary vulnerability—an elevation of privilege (EoP) flaw in the operating system kernel or a system service running outside the sandbox. In the campaign mounted by UTA0560, the attackers successfully identified and paired two previously unknown vulnerabilities that satisfied these exact criteria.
The intrusion sequence initiated through meticulously crafted spear-phishing messages sent to high-value individuals within targeted organizations. These messages contained links leading to compromised or attacker-controlled websites hosting the malicious framework. When a victim navigated to the link using an unpatched Chrome browser, the initial zero-day vulnerability triggered immediately. This component exploited a remote code execution (RCE) flaw within Chrome's V8 JavaScript engine, granting the attackers control over the browser's renderer process.
Once inside the renderer, the exploit payload immediately targeted the second zero-day: a kernel-level vulnerability within Microsoft Windows. By exploiting this flaw, the malicious code escaped Chrome's sandbox protections and achieved arbitrary code execution with elevated system privileges. With full control over the host environment, the attackers dropped and executed their primary surveillance implant.
Unmasking GRIMWEDGE: The Next-Gen JavaScript Backdoor
The ultimate goal of this intricate exploit chain was the covert deployment of GRIMWEDGE, a newly identified malware family that demonstrates the evolving stealth techniques employed by modern threat actors. Unlike traditional backdoors written in compiled languages like C or C++, GRIMWEDGE relies heavily on JavaScript and native host execution environments such as Windows Script Host or Node.js runtimes.
GRIMWEDGE acts as an initial access foothold and intelligence-gathering framework. Its design focuses on minimalism, modularity, and evasiveness. By operating largely within legitimate system processes and utilizing lightweight script-based payloads, it effectively avoids detection by conventional signature-based antivirus engines.
Upon initial execution, GRIMWEDGE performs rigorous environment checks to ensure it is not running inside a analyst's sandbox or virtual machine. It checks system uptime, active process lists, registry keys, and network interface configurations. If any indication of analysis software is detected, the malware quietly terminates its process without dropping secondary files, preserving the attackers' operational security.
If the host system is verified as a legitimate target, GRIMWEDGE establishes persistence using standard Windows persistence mechanisms, such as scheduled tasks or modified registry run keys. It then initiates encrypted command-and-control (C2) communications over HTTPS, disguising its traffic within routine web requests. The backdoor supports a standard array of espionage capabilities, including:
- Executing arbitrary system commands and shell scripts.
- Gathering detailed hardware, network, and user profile telemetry.
- Enumerating local files, directories, and connected network drives.
- Exfiltrating sensitive documents and stolen authentication tokens.
- Downloading secondary payloads, such as credential dumpers or lateral movement tools.
The Strategic Objective: Why Target NGOs?
While corporate networks and government agencies are standard targets for state-backed cyber espionage, non-governmental organizations occupy a uniquely critical position in the global geopolitical ecosystem. Threat actors frequently focus on NGOs, human rights groups, think tanks, and foreign policy institutes to gain early visibility into policy shifts, civil rights movements, and international diplomatic strategies.
NGOs often operate on limited cybersecurity budgets compared to commercial enterprises or national defense departments. This creates a dangerous imbalance: these organizations possess high-value intelligence regarding international affairs, human rights abuses, and global policy, yet they often lack the dedicated security operations centers (SOCs) necessary to identify advanced threats.
For state-aligned threat actors like UTA0560, targeting NGOs yields significant strategic returns with relatively lower risk of immediate detection. Intercepting communications within these organizations provides state intelligence agencies with advance notice regarding international advocacy campaigns, foreign political aid distribution, and policy white papers that could influence international sanctions or trade agreements.
The Rising Costs of the Zero-Day Market
The discovery of a dual zero-day exploit chain deployed in the wild highlights a growing concern for security teams globally: the increasing accessibility and economic value of zero-day vulnerabilities. Historically, zero-days were reserved exclusively for nation-states executing critical military or espionage operations due to the immense cost and effort required to discover and maintain them.
Today, a booming commercial surveillance industry and offensive vulnerability market have shifted these dynamics. Browser remote code execution zero-days routinely command prices exceeding one million dollars on the private market, while Windows local privilege escalation flaws can fetch hundreds of thousands of dollars. Deploying two such flaws simultaneously in a single phishing campaign represents a multi-million-dollar operational expenditure.
The willingness of actors like UTA0560 to burn high-value zero-day vulnerabilities against NGO targets indicates one of two possibilities: either these threat groups possess vast internal vulnerability research capabilities that allow them to discover zero-days at scale, or the strategic imperative behind monitoring these targets was deemed valuable enough to justify burning multi-million-dollar assets before vendors could patch them.
Defending Against Full-Chain Exploits
The reliance on zero-day chains fundamentally challenges traditional security paradigms that rely on patch management as a primary defensive shield. While applying software updates as soon as they become available remains crucial, zero-day attacks by definition target flaws for which no patch yet exists.
To mitigate the risk posed by zero-day exploit chains and stealthy implants like GRIMWEDGE, organizations must implement defense-in-depth architecture:
- Attack Surface Reduction: Organizations handling sensitive geopolitical data should consider deploying strict application control policies. Disabling unnecessary script hosts like Windows Script Host (WSH) or constraining PowerShell capabilities significantly reduces the execution avenues available to script-based implants like GRIMWEDGE.
- Behavioral EDR Monitoring: Because traditional antivirus signatures fail against novel exploits and backdoors, Endpoint Detection and Response (EDR) solutions must focus on behavioral anomalies. Detecting browser processes spawning unexpected child processes or invoking privileged system APIs provides critical detection opportunities during the sandbox escape phase.
- Network Micro-segmentation: Restricting outbound network connections from endpoint devices ensures that even if an attacker successfully deploys a backdoor, C2 channels cannot easily be established to unauthorized external IP addresses.
- Hardware-Enforced Isolation: Utilizing micro-virtualization techniques—such as running web browsers within temporary, hardware-isolated virtual machines—ensures that even a full RCE and sandbox escape fails to compromise the underlying persistent operating system.
What Lies Ahead
The discovery of UTA0560's campaign highlights the relentless pace of offensive security research by state-sponsored actors. As vendors like Google and Microsoft continue to harden their codebases and implement sophisticated memory safety features like Rust adoption, attackers are forced to innovate, pairing multiple specialized vulnerabilities together to achieve their goals.
For enterprise security teams and civil society organizations alike, the lesson is clear: relying solely on basic patch management is no longer sufficient against targeted state-sponsored threat groups. Proactive threat hunting, robust behavioral monitoring, and defensive isolation technologies must become standard components of modern cybersecurity strategies if organizations hope to withstand the next generation of zero-day exploits.